ChatGPT
 Perplexity
 Claude
 Grok
 Google AI Mode
The first time I wired a PHP popup into a real product, I was a junior engineer at Oracle, and the "popup" was a JavaScript alert() echoed out of a PHP error handler. It worked. It also looked exactly as ugly as you'd expect. Years later the question hasn't gone away: developers still ask how do I trigger a popup from PHP? The answer in 2026 is sharper than it was. Every code block below was run on PHP 8.3 and PHP 8.5 and tested in Chrome (checked October 2026).
What you'll need:
• A PHP environment: Local (XAMPP, MAMP, Laravel Herd) or any host running PHP 8.3 or newer. PHP 8.5 is the current release.
• Basic syntax familiarity: You should be comfortable with echo, variables, sessions and where to place a script tag.
• A test page: Any .php file you can load in a browser.
• Time: 15-30 minutes to get all four popup types running.
• Skill level: Beginner-friendly. If you can write a "Hello, World" in PHP, you can ship this.
What Is a PHP Popup in 2026?
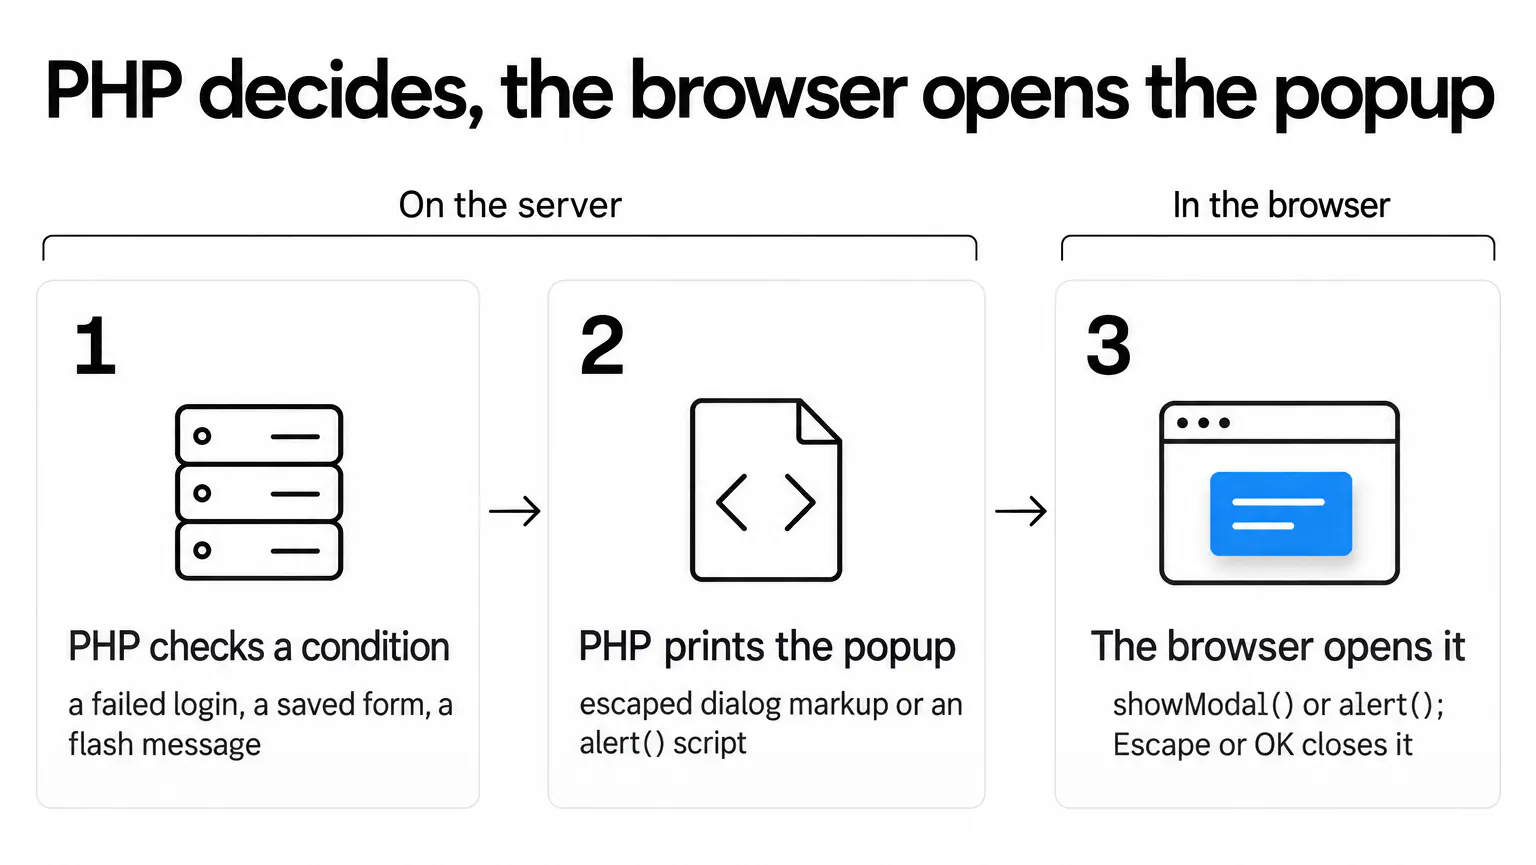
A PHP popup is a small browser dialog (an alert, confirm or prompt window) or a styled modal whose appearance is decided by PHP code. The important part: PHP doesn't actually open the window. PHP is a server-side language. It runs on the server, generates HTML, and sends the result to the browser. The browser is what opens the popup, using the JavaScript or the <dialog> markup that PHP printed into the response.
So when developers say "PHP popup," what they really mean is a JavaScript or HTML popup, triggered by a PHP condition. The PHP file decides whether the popup should appear and what it says. The browser handles the opening, closing and styling, with JavaScript and CSS. That distinction matters more in 2026 than it did five years ago, because modern best practice is to keep server logic and client interactivity in their own lanes.
The PHP ecosystem is still enormous, but it's gone gray at the edges. According to Perforce's 2026 PHP report (April 2026, a survey of more than 700 open source users), over half of surveyed PHP users have more than 15 years of experience with the language, while only 15% have five years or less. Translation: many of the people maintaining PHP popup code today learned the pattern when echoing JavaScript was normal. It's still common in WordPress plugins, Laravel admin panels, and legacy LAMP apps, but the modern version of this pattern is cleaner, and the steps below show it.
Why Use a PHP Popup on Your Website?
The use case is narrower than most tutorials admit. PHP popups are useful when:
• Form validation feedback: A user submits a form, PHP validates it server-side, and if something fails, you show a popup with the error on the page that comes back. This is the single most common real-world use.
• Confirmation after a server action: "Your password has been updated" or "Record deleted," shown right after the PHP handler finishes.
• Warnings tied to server state: Stock running low, session expiring, role-based alerts. The condition lives on the server; the message has to reach the browser.
• Quick admin tools: Internal CRUD pages where you don't need a fancy modal system. A one-line alert() is faster to write than a Bootstrap modal.
Most of the searches that bring developers to this page ask a version of the same question: php popup message, php alert, php message box. In other words, how do I show a message from my backend? A PHP popup answers that with a few lines of code. That's its real value.
Where it falls short: anything that needs styling, animation, mobile responsiveness, A/B testing, or analytics. Those belong in a proper popup system, not an echoed alert(). A <dialog> that PHP renders (Step 4) covers the styling. The Popupsmart section covers the rest of that trade-off.
How to Create a PHP Popup: The Three Core Methods
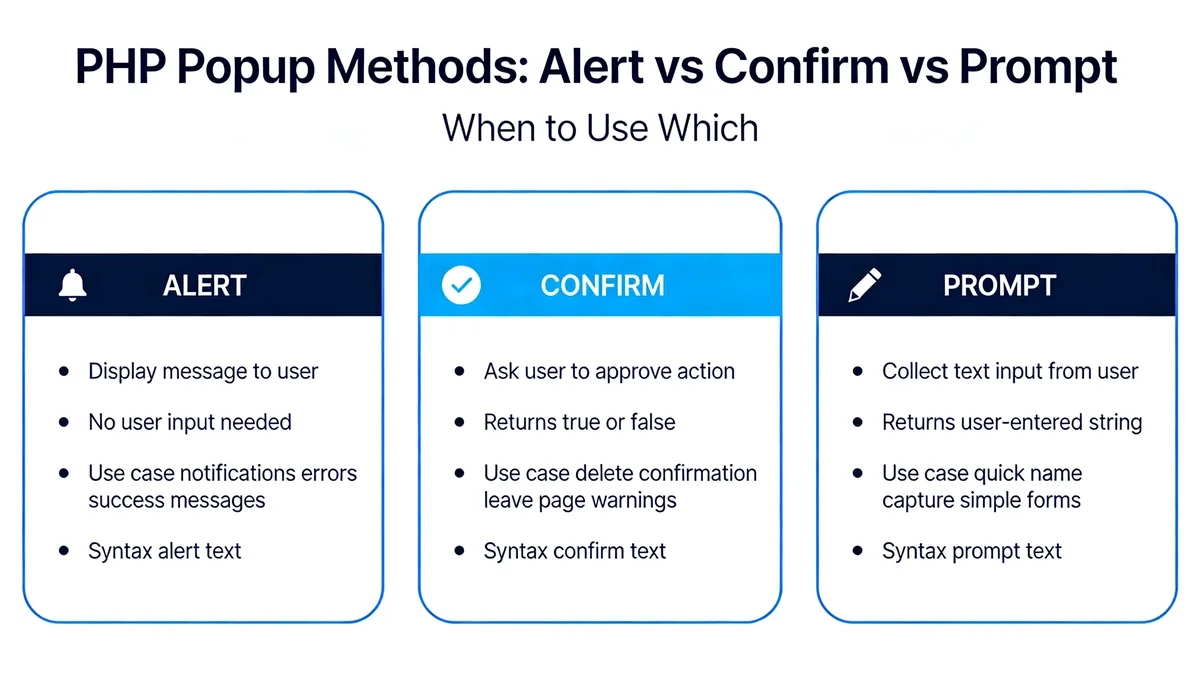
PHP gives you three native browser dialog primitives to work with, each via JavaScript: alert(), confirm(), and prompt(). Each one solves a different interaction problem. The quick decision guide: use Alert for one-way messages, Confirm for yes/no decisions, and Prompt for short text input. If you need more than that, you've outgrown the native dialogs and should jump to Step 4, where PHP renders a styled HTML <dialog>, or to the Laravel and Popupsmart sections below.
Quick overview of the methods:
| Method | What it does | Good for |
|---|---|---|
| 1. PHP Alert Window | One-way message to the user. They click OK and continue. | Notifications, errors, success messages |
| 2. PHP Confirm Window | Asks the user a yes/no question. Returns true or false to JavaScript. | "Are you sure?" actions |
| 3. PHP Prompt Window | Asks the user for a short text input. Returns the typed string, or null. | A short value in an internal tool |
4. Custom <dialog> popup |
Shows your own HTML and CSS as a modal, opened with showModal(). |
Anything customers see: styled messages, forms, offers |
For a similar walkthrough in other languages, our Python popup guide covers the same three patterns with Tkinter, and the Angular popup guide shows how the modern framework version compares.
Step 1: Build a PHP Alert Window
The alert window is the simplest of the three. It displays a single message and an OK button. The user has to dismiss it before they can interact with the rest of the page. PHP injects it by echoing a <script> tag containing alert().
Detailed Instructions
1. Create a new PHP file and call it alert-popup.php.
2. Inside the file, write a PHP block that echoes a script tag with the alert() call:
<?php echo "<script>alert('Welcome to our site!');</script>"; ?>
3. Save the file and load it through your local server (e.g., http://localhost/alert-popup.php).
4. The browser parses the PHP output, sees the script tag, and immediately fires the alert(). The popup appears on page load.
To make it conditional (which is the whole point of using PHP in the first place), wrap it in an if statement, and pass the message through json_encode() so quotes and tags can't break the script:
<?php
declare(strict_types=1);

$loginFailed = true; // set by your own login check
$message = 'Invalid credentials. Please try again.';

if ($loginFailed): ?>
<script>
  alert(<?= json_encode($message, JSON_HEX_TAG | JSON_HEX_AMP | JSON_HEX_APOS | JSON_HEX_QUOT | JSON_THROW_ON_ERROR) ?>);
</script>
<?php endif; ?>
json_encode() turns the PHP string into a valid JavaScript string literal, quotes included. The four JSON_HEX_* flags convert <, >, &, ' and " into \u escapes, so a message containing </script> can't close your script tag early. JSON_THROW_ON_ERROR makes a bad value (invalid UTF-8, for example) throw an exception instead of printing nothing.
Expected Result
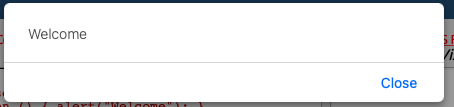
You'll know it's working when: The page loads, and a native browser dialog appears with your message and a single OK button. The dialog blocks the rest of the page until dismissed.
Common Mistakes & Troubleshooting
• Quotes inside the message break the script: If your message contains an apostrophe (e.g., "It's a test") and you paste it into a single-quoted JavaScript string by hand, the JavaScript syntax breaks and the console reports an unexpected identifier. Don't escape by hand: build the string in PHP and print it with json_encode(), as in the example above. It adds the quotes and escapes everything inside them.
• The popup fires before the page renders: An alert echoed at the top of the file fires before the rest of the HTML loads, leaving a blank page behind it. If you want the page visible first, place the script just before </body>, or wrap the call in document.addEventListener('DOMContentLoaded', () => { ... }).
• Browser pop-up blockers: Native alert() is rarely blocked, but window.open() popups (a different beast) almost always are. If your "popup" never appears, check that you're using alert(), not window.open().
Pro Tip
Pro tip: The cleanest pattern I've landed on is to never echo raw JavaScript strings with user input in them. Always pass server values through json_encode() first, with the JSON_HEX_* flags, e.g., echo '<script>alert(' . json_encode($message, JSON_HEX_TAG | JSON_HEX_AMP | JSON_HEX_APOS | JSON_HEX_QUOT) . ');</script>';. It handles escaping correctly, prevents XSS, and works with apostrophes, quotes, and unicode without you thinking about it.
Step 2: Build a PHP Confirm Window
The confirm window asks a yes/no question and returns a boolean to JavaScript. You'd reach for it when the user is about to do something destructive: delete a record, cancel a subscription, close an account. PHP renders the form; JavaScript asks the question; PHP does the work only after a real request arrives.
Detailed Instructions
1. Create a file called confirm-popup.php.
2. Render a POST form for the action and attach confirm() to its submit event. Cancel stops the form; OK lets it through. The hidden CSRF token proves the request came from your page:
<?php
declare(strict_types=1);
session_start();
$_SESSION['csrf'] ??= bin2hex(random_bytes(32));
$itemId = 42; // the record this button deletes
?>
<form method="post" action="delete.php" id="delete-form">
  <input type="hidden" name="id" value="<?= htmlspecialchars((string) $itemId) ?>">
  <input type="hidden" name="csrf" value="<?= htmlspecialchars($_SESSION['csrf']) ?>">
  <button type="submit">Delete item</button>
</form>

<script>
  document.getElementById('delete-form').addEventListener('submit', (event) => {
    if (!confirm('Are you sure you want to delete this item?')) {
      event.preventDefault(); // Cancel: the form is not sent
    }
  });
</script>
3. Create delete.php. It refuses anything that isn't a POST with the right token, does the work, stores a message for the next page and redirects:
<?php
declare(strict_types=1);
session_start();

$token = (string) ($_POST['csrf'] ?? '');
if ($_SERVER['REQUEST_METHOD'] !== 'POST' || !hash_equals($_SESSION['csrf'] ?? '', $token)) {
    http_response_code(403);
    exit('Request refused.');
}

$id = filter_input(INPUT_POST, 'id', FILTER_VALIDATE_INT);
// Delete the record with $id here.

$_SESSION['flash'] = 'Item deleted.';
header('Location: /items.php', true, 303);
exit;
4. Open confirm-popup.php in the browser and click the button. The confirm dialog appears with OK and Cancel buttons. Cancel keeps you on the page; OK sends the form, and delete.php redirects to items.php, where Step 4 shows the "Item deleted." message as a popup.
Expected Result
You'll know it's working when: A native browser dialog appears with your question and two buttons, OK and Cancel. Clicking OK sends the form; Cancel sends nothing. Opening delete.php directly in the address bar returns "Request refused."
Common Mistakes & Troubleshooting
• Confusing client-side and server-side logic: The confirm() result lives entirely in the browser. PHP has already finished running by the time the user clicks OK or Cancel. If you want the server to act on the choice, the JavaScript branch has to make a follow-up request (form submit, fetch, redirect). Reading the confirm result in a PHP if can't work: that request is already done.
• Treating confirm() as protection: Anyone can send the POST request without ever seeing your dialog. The server has to check the method and the CSRF token, as delete.php does. Never delete anything on a plain GET link, because browsers, crawlers and link previews follow links.
• Forgetting to escape the message: Same trap as alert. If the question includes dynamic content, wrap it in json_encode() before injecting it into JavaScript.
Pro Tip
Pro tip: Confirm dialogs are accessibility-friendly out of the box: screen readers announce them, keyboard users can dismiss them with Escape, and they take focus when they open. That's why I still reach for them on internal admin tools. But for customer-facing destructive actions, build a proper modal with a typed confirmation ("type DELETE to continue"). Native confirm is too easy to click through on autopilot.
Step 3: Build a PHP Prompt Window
The prompt window asks the user for a short text input. It returns the typed string to JavaScript, or null if the user clicks Cancel. PHP serves the page that triggers it, then reads the answer on the next request.
Detailed Instructions
1. Create a file called prompt-popup.php.
2. Add a script that calls prompt() and sends the answer to the next page:
<script>
  const visitorName = prompt('Please enter your name:', '');
  if (visitorName !== null && visitorName.trim() !== '') {
    window.location.href = 'welcome.php?name=' + encodeURIComponent(visitorName.trim());
  }
</script>
3. Save and load the page. The prompt appears with a text field and OK / Cancel buttons.
4. When the user submits, the script appends the value to the URL and redirects to welcome.php, where PHP reads it from the query string and prints it escaped:
<?php
declare(strict_types=1);

$name = trim((string) filter_input(INPUT_GET, 'name'));
?>
<p>Welcome to Popupsmart, <?= htmlspecialchars($name !== '' ? $name : 'friend') ?>!</p>
Expected Result
You'll know it's working when: The browser opens a dialog with a text input field, OK, and Cancel. The user types a value, clicks OK, and the URL changes to include their input. PHP on the destination page reads the value and personalizes the response ("Welcome to Popupsmart, Ann!"). Typed HTML shows up as plain text, not as markup.
Common Mistakes & Troubleshooting
• Treating prompt input as trusted: Anything the user types is a string they fully control. Don't echo it back into the page unescaped: use htmlspecialchars() on the receiving side, as welcome.php does.
• Sending the answer in the URL: A query string ends up in browser history and server logs. That's fine for a first name. For anything private or longer than a short answer, post it with a form instead.
• The prompt feels dated: Native prompts look like Windows 95. For anything customer-facing, you want a styled modal with an input field: see Step 4 and the Popupsmart section below.
Pro Tip
Pro tip: If you're using prompt to collect emails or names for a marketing list, stop. Native prompts have zero conversion data attached to them: no impressions, no completion rate, no drop-off tracking. Native prompt is fine for internal tools and quick prototypes. For acquisition, build it properly.
Step 4: Build a Custom PHP Popup with the HTML Dialog Element
A custom PHP popup is a <dialog> element that PHP renders into the page with its text escaped, opened and closed by a few lines of JavaScript and styled with CSS. It's the version to use for anything customers see, because you control the design and the browser handles the accessibility.
The split is the same as before: PHP decides and prints, the browser opens. What changes is that the popup is your own HTML. showModal() puts it in the top layer, makes the rest of the page inert, closes it on Escape, and exposes it to screen readers as a modal dialog, according to MDN's dialog element reference. The element has worked across major browsers since March 2022.
Detailed Instructions
1. Create items.php, the page delete.php redirects to. It reads the flash message once, deletes it, and renders a dialog only when there is one. A second dialog opens from a button:
<?php
declare(strict_types=1);
session_start();

// Set by the handler that ran before the redirect (delete.php above)
$flash = $_SESSION['flash'] ?? null;
unset($_SESSION['flash']);

function e(string $value): string
{
    return htmlspecialchars($value, ENT_QUOTES | ENT_SUBSTITUTE, 'UTF-8');
}
?>
<!doctype html>
<html lang="en">
<head>
  <meta charset="utf-8">
  <title>Items</title>
  <link rel="stylesheet" href="/popup.css">
  <script src="/popup.js" defer></script>
</head>
<body>
  <main>
    <button type="button" data-popup="newsletter-popup">Get the newsletter</button>
  </main>

  <?php if (is_string($flash) && $flash !== ''): ?>
  <dialog id="flash-popup" class="popup" aria-labelledby="flash-popup-title" data-open-on-load>
    <div>
      <h2 id="flash-popup-title">Done</h2>
      <p><?= e($flash) ?></p>
      <form method="dialog">
        <button autofocus>OK</button>
      </form>
    </div>
  </dialog>
  <?php endif; ?>

  <dialog id="newsletter-popup" class="popup" aria-labelledby="newsletter-popup-title">
    <div>
      <h2 id="newsletter-popup-title">Get one email a month</h2>
      <form method="post" action="/subscribe.php">
        <label for="email">Email</label>
        <input id="email" name="email" type="email" required autocomplete="email">
        <button type="submit">Subscribe</button>
      </form>
      <form method="dialog">
        <button aria-label="Close">×</button>
      </form>
    </div>
  </dialog>
</body>
</html>
2. Create popup.js. It opens every dialog.popup on load or on a button click, closes it on a backdrop click, and sends focus back to the button that opened it:
// Opens the <dialog> popups PHP rendered: on page load (data-open-on-load)
// or when a button with data-popup="<dialog id>" is clicked.
for (const dialog of document.querySelectorAll('dialog.popup')) {
  let opener = null;

  // Escape and <form method="dialog"> close it natively; send focus back.
  dialog.addEventListener('close', () => opener?.focus());

  // A click on the backdrop lands on the <dialog> itself, not its inner <div>.
  dialog.addEventListener('click', (event) => {
    if (event.target === dialog) dialog.close();
  });

  for (const button of document.querySelectorAll(`[data-popup="${dialog.id}"]`)) {
    button.addEventListener('click', () => {
      opener = button;
      dialog.showModal();
    });
  }

  if (dialog.hasAttribute('data-open-on-load')) dialog.showModal();
}
3. Create popup.css. The dialog has no padding of its own (the inner div carries it), which is what makes the backdrop-click check in popup.js reliable:
.popup {
  width: min(28rem, calc(100vw - 2rem));
  padding: 0;
  border: 0;
  border-radius: 12px;
  box-shadow: 0 20px 50px rgb(0 0 0 / 0.25);
}
.popup > div { padding: 1.5rem; }
.popup::backdrop { background: rgb(0 0 0 / 0.5); }

.popup[open] { animation: popup-in 200ms cubic-bezier(0.23, 1, 0.32, 1); }
@keyframes popup-in {
  from { opacity: 0; transform: translateY(8px); }
}
@media (prefers-reduced-motion: reduce) {
  .popup[open] { animation: none; }
}
4. Run the Step 2 flow again: delete the item, and items.php opens with the "Item deleted." popup. Refresh, and it's gone, because the message was removed from the session. This is the Post/Redirect/Get pattern, and it's the clean answer to "how do I show a PHP alert message after a form is submitted."
Expected Result
You'll know it's working when: The flash popup opens over a dimmed page with focus on OK. Escape, OK, or a click on the dimmed backdrop closes it. "Get the newsletter" opens the second popup with focus in the email field; closing it puts focus back on the button. At 375px wide the popup keeps a 1rem margin on each side. With reduced motion turned on in the operating system, it appears without the slide.
Common Mistakes & Troubleshooting
• Using the open attribute instead of showModal(): <dialog open> shows the element but not as a modal: no backdrop, no inert page, no Escape. Open it with showModal().
• The flash popup shows on every refresh: Delete the message from the session after reading it (unset($_SESSION['flash'])), and redirect after the POST instead of rendering the result page directly.
• Escaping in the wrong place: Escape at the moment you print, with htmlspecialchars() for HTML and json_encode() for JavaScript. Escaping when you store the value means double-escaped text in one place and none in another.
For more modal patterns in plain HTML, CSS, Bootstrap and Tailwind, see our guide on how to create modal popups.
PHP 8+ Compatibility and Security Best Practices for Popups
If you're writing new PHP popup code in 2026, you should be on PHP 8.x, and 8.3 or newer for anything new. According to php.net's supported versions page, PHP 8.5 was released on 20 November 2025, and PHP 8.3 gets security fixes until 31 December 2027. Laravel 13 needs PHP 8.3 at minimum, so most framework code is landing on 8.3 through 8.5 right now.
A few things to watch:
• Stricter type handling: PHP 8 enforces types more aggressively than 7.x. Since PHP 8.1, passing null to a built-in function like htmlspecialchars() raises a deprecation notice. If your popup message can be missing, check for it before you print, as items.php does with is_string($flash).
• Escaping defaults: Since PHP 8.1, htmlspecialchars() escapes single and double quotes by default (ENT_QUOTES | ENT_SUBSTITUTE | ENT_HTML401). Passing the flags and 'UTF-8' explicitly, as the e() helper does, keeps the behavior obvious to whoever reads the code next.
• JIT compilation: PHP 8's JIT mostly helps CPU-bound workloads. Echoing strings doesn't see much of a difference, but if your popup is gated behind a complex query, the surrounding logic gets faster.
• Always sanitize user input: XSS via popup is one of the oldest bugs in the PHP world. Wrap any dynamic content with json_encode() and the JSON_HEX_* flags on its way into a script tag, and htmlspecialchars() on its way into HTML. If you forget one of those, you've shipped a vulnerability.
• Actions need a POST and a token: A popup that confirms an action is only the question. The action itself runs on a POST request with a CSRF token checked by hash_equals(), as in Step 2.
There's no single headline feature to chase in 2026. The language got faster and stricter at the same time. Your old popup code will probably still run on 8.5, but it's worth re-reading it to make sure you're not echoing untyped user input or relying on PHP 7.x's looser comparisons.
Integration with Modern PHP Frameworks like Laravel
If you're working in a Laravel codebase, or any other modern PHP framework, you probably don't want to be writing inline echo "<script>" statements. The framework idiom is to flash the message in the controller and render the popup in a Blade template.
In Laravel 13 (checked against the Laravel 13 docs, October 2026), the controller flashes the message while redirecting:
<?php

namespace App\Http\Controllers;

use App\Http\Requests\ProfileUpdateRequest;
use Illuminate\Http\RedirectResponse;

class ProfileController extends Controller
{
    public function update(ProfileUpdateRequest $request): RedirectResponse
    {
        $request->user()->update($request->validated());

        return redirect()
            ->route('profile.edit')
            ->with('popup', 'Profile updated successfully.');
    }
}
ProfileUpdateRequest stands for your own form request. Then in your Blade layout, render the same <dialog> as Step 4. Blade's {{ }} escapes the message for you:
@if (session('popup'))
    <dialog id="flash-popup" class="popup" aria-labelledby="flash-popup-title" data-open-on-load>
        <div>
            <h2 id="flash-popup-title">Saved</h2>
            <p>{{ session('popup') }}</p>
            <form method="dialog">
                <button autofocus>OK</button>
            </form>
        </div>
    </dialog>
@endif
Load popup.js and popup.css from Step 4 in the layout and you're done. That keeps the popup trigger out of your view logic, works with Laravel's CSRF protection and session flash messages without extra wiring, and never prints unescaped data with {!! !!}.
For complex popups inside a Laravel app, the usual routes are Livewire or Inertia.js with your component library of choice. The PHP side just sets state; the frontend handles rendering. This is the same separation-of-concerns story that's been creeping into PHP land for years, and it's why "echo a script tag" is a fine quick fix but a bad long-term pattern.
WordPress is PHP too, with its own helpers for the same two jobs: esc_html() for text in HTML and wp_json_encode() for data going into a script.
If you're integrating popups into other frameworks, the equivalent guides for React popups and Bootstrap modal popups walk through the framework-native versions.
Try Popupsmart For Creating Popups Without Echoing JavaScript
First, where this fits. If you're building an in-app PHP modal (a confirmation inside a Laravel admin panel, a server-side validation alert, a quick prompt), you do not need Popupsmart. The methods above are the right tool. They run inside your app, they respond to your server state, and they ship in a few lines of code.
Where Popupsmart earns its place is the other side of the popup problem: marketing popups on your public site. Exit-intent campaigns, email opt-ins, discount offers, announcement bars. The stuff your marketing team wants to A/B test without filing a ticket with engineering. I'm Popupsmart's COO, so weigh my view accordingly.
If that's your use case, here's how it works:
Sign up for Popupsmart and head to your dashboard.
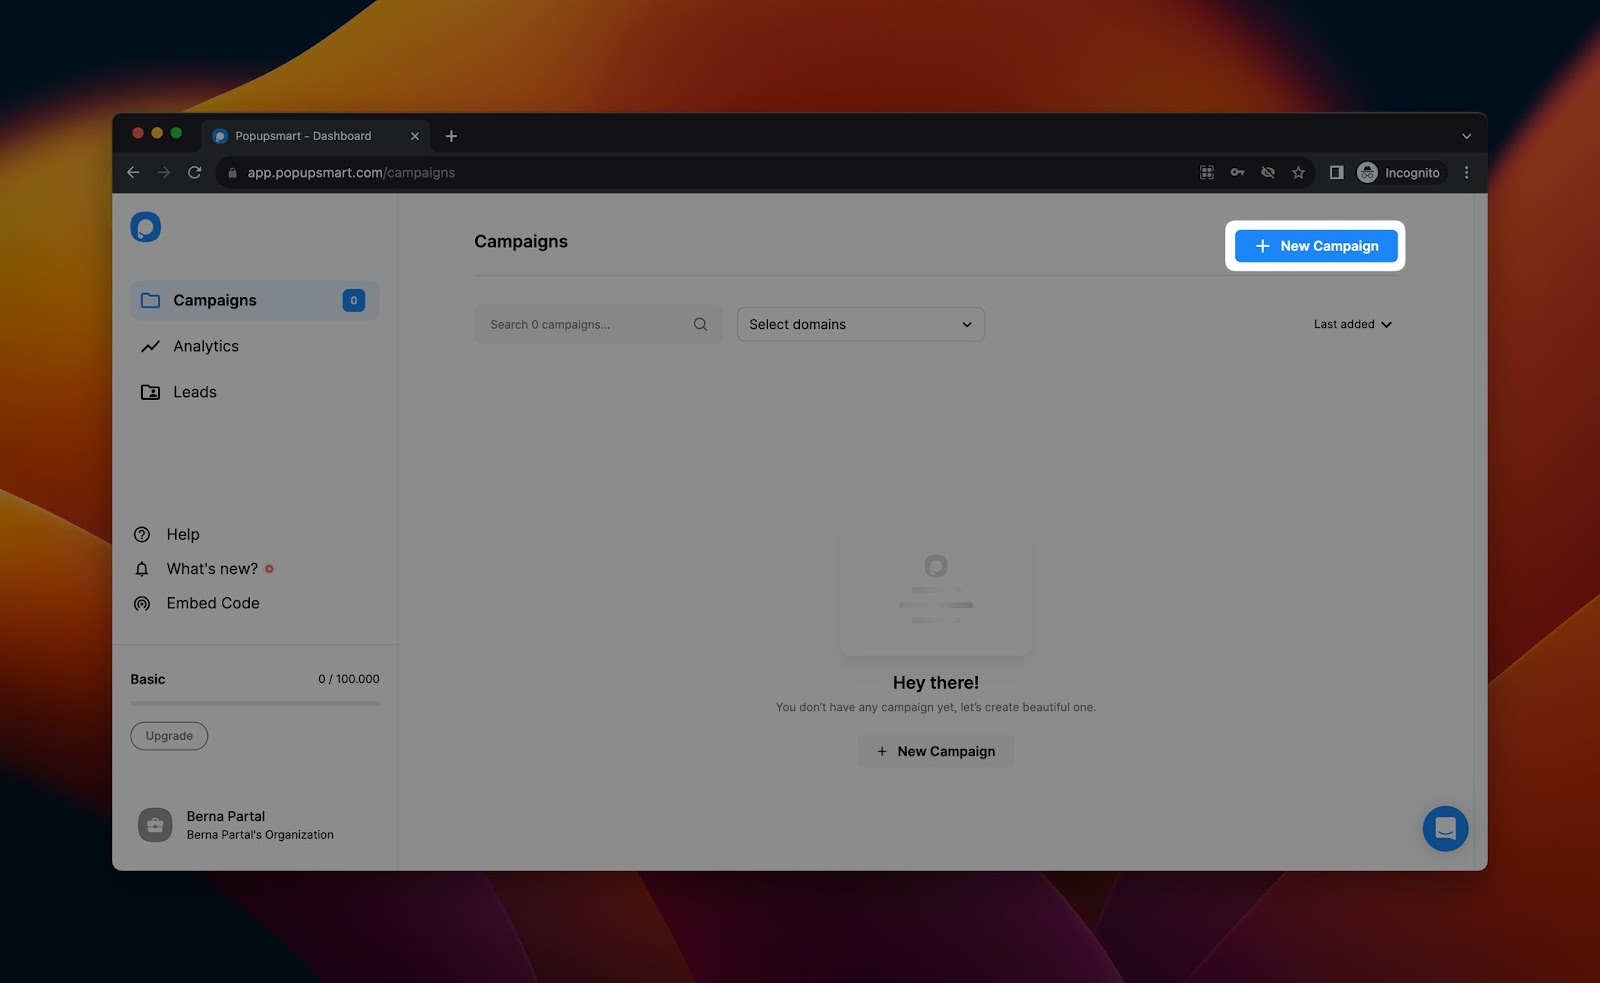
1. Click "New Campaign" on the dashboard.
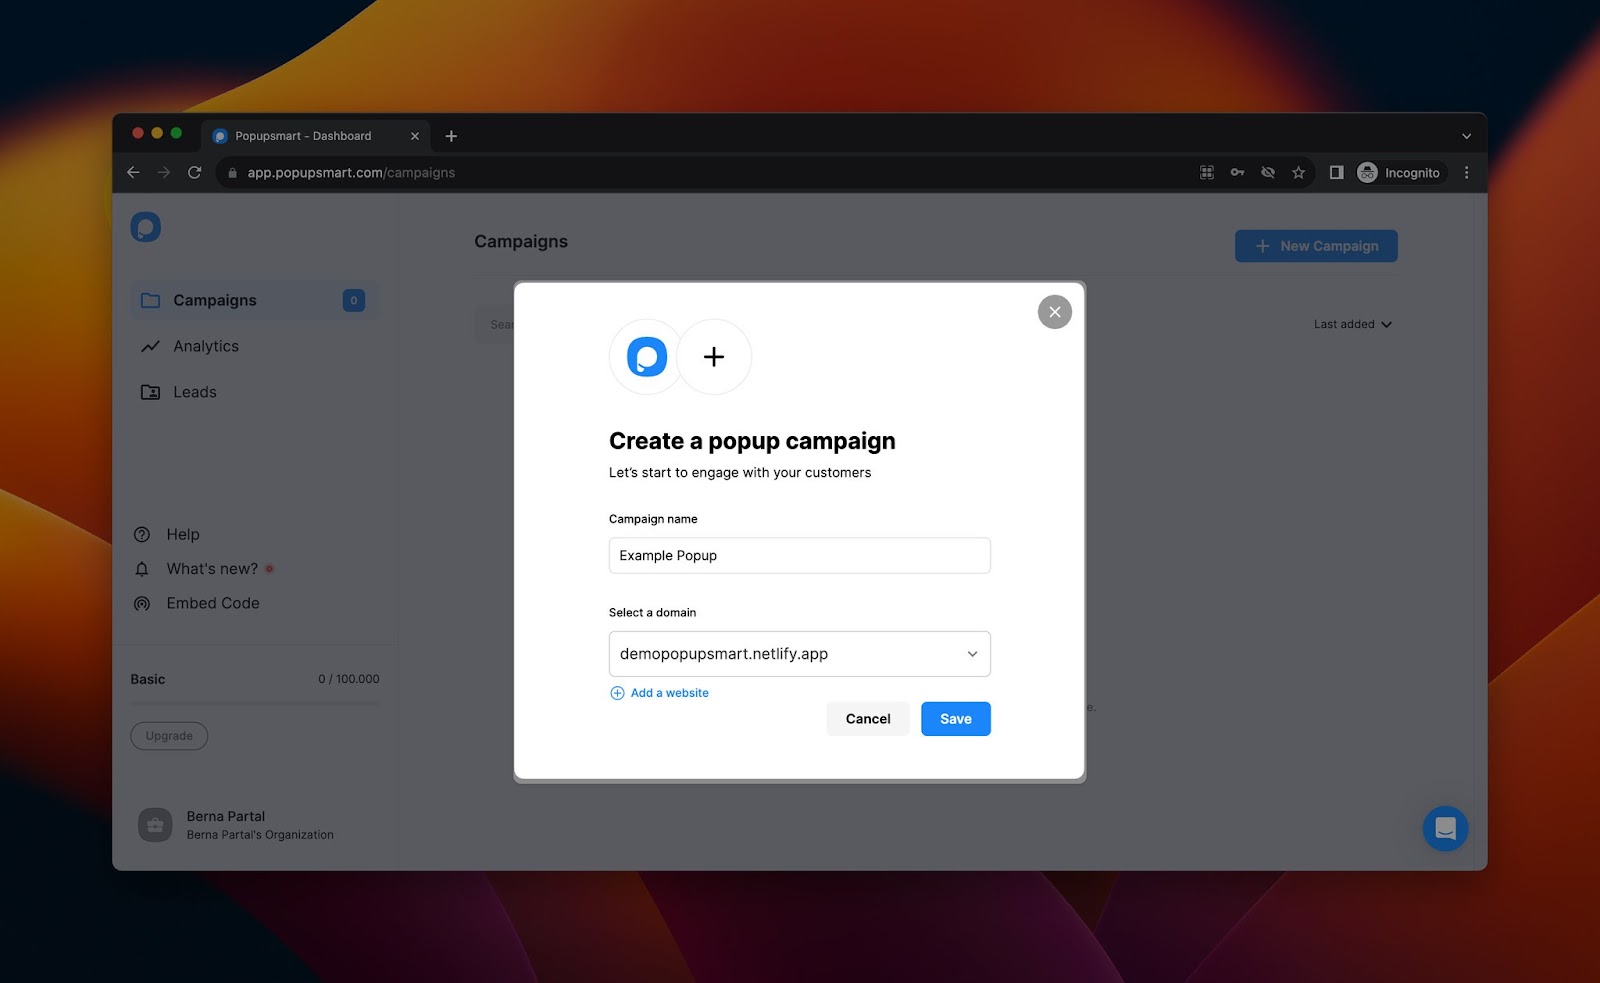
2. Name your campaign, select your domain and save.
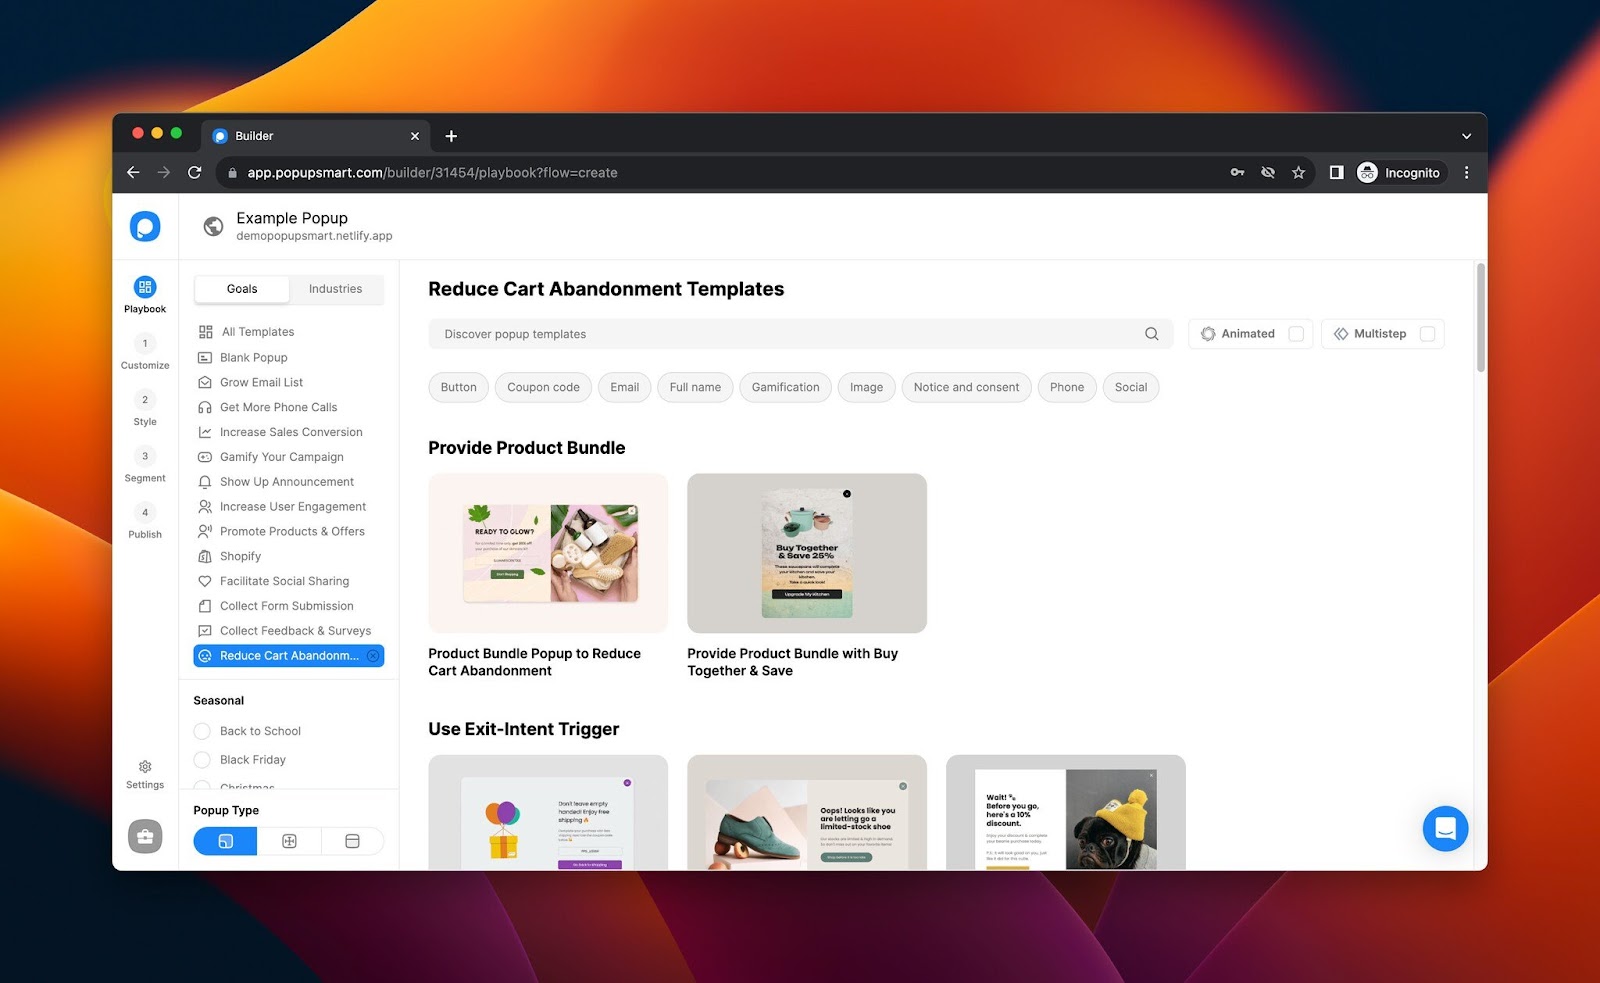
3. Pick a template from the Playbook section. Choose your goal (email capture, exit-intent, discount, etc.) and pick a popup template that fits. You can browse the same popup templates before you sign up.
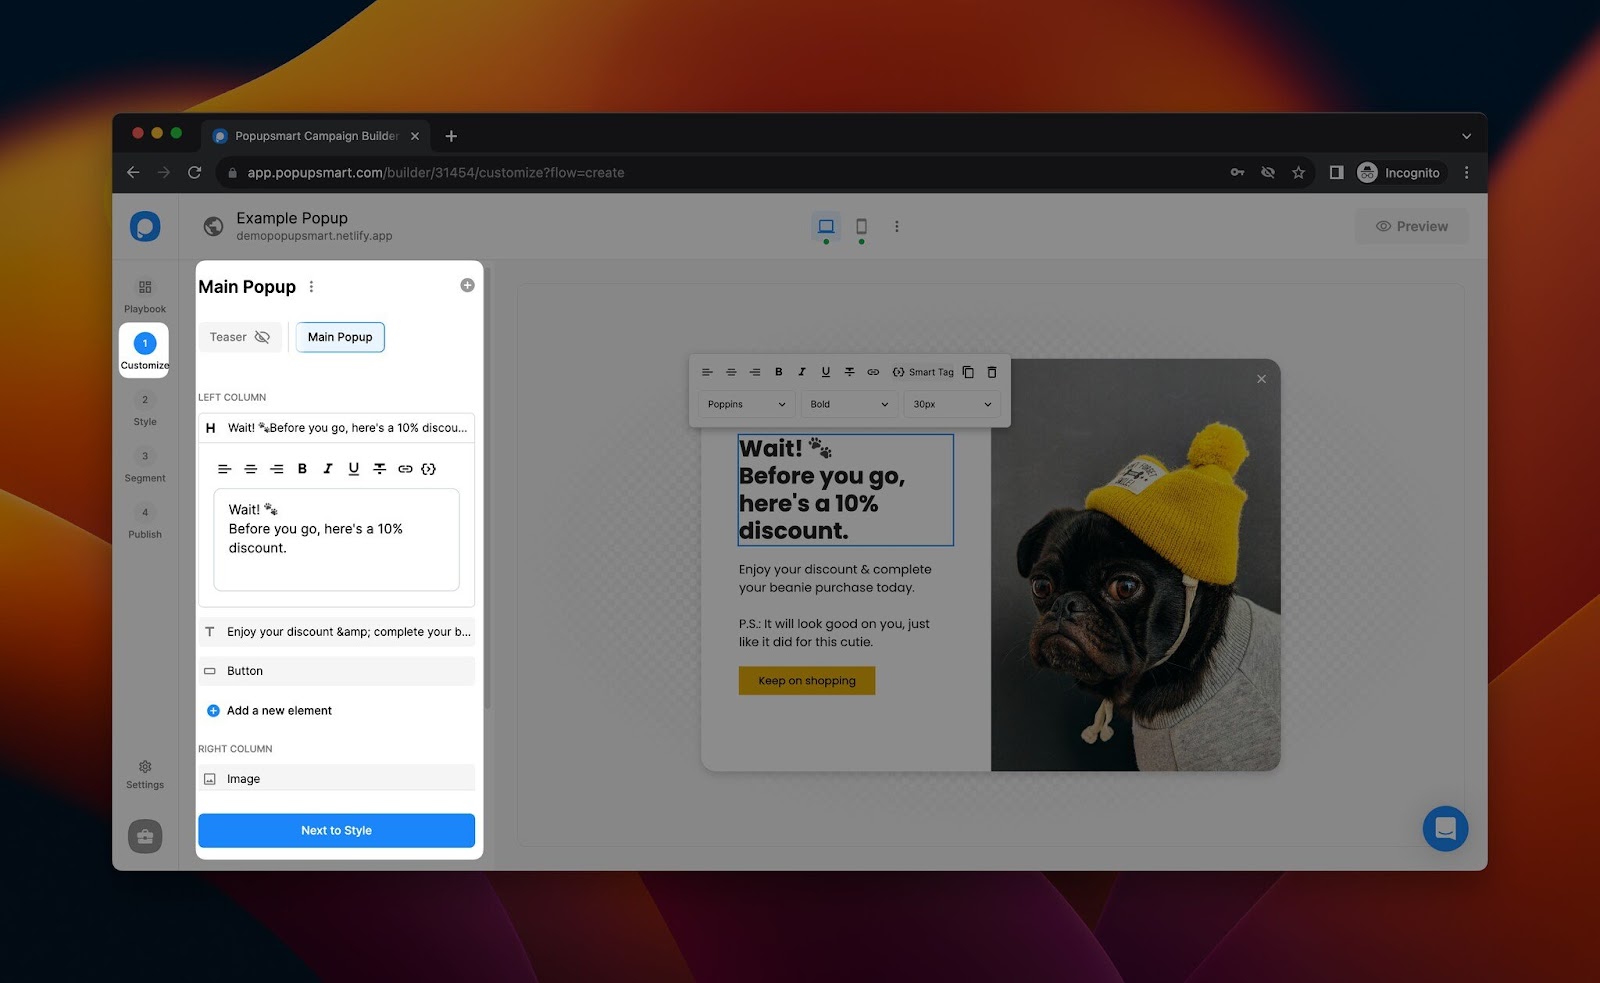
4. Customize the design. Edit headline, body, CTA button, image. The Style section is where you adjust the look and the popup's size.
5. Configure targeting in the Segment section. Choose audience, behavior triggers (time on page, scroll depth, exit-intent), and frequency caps.
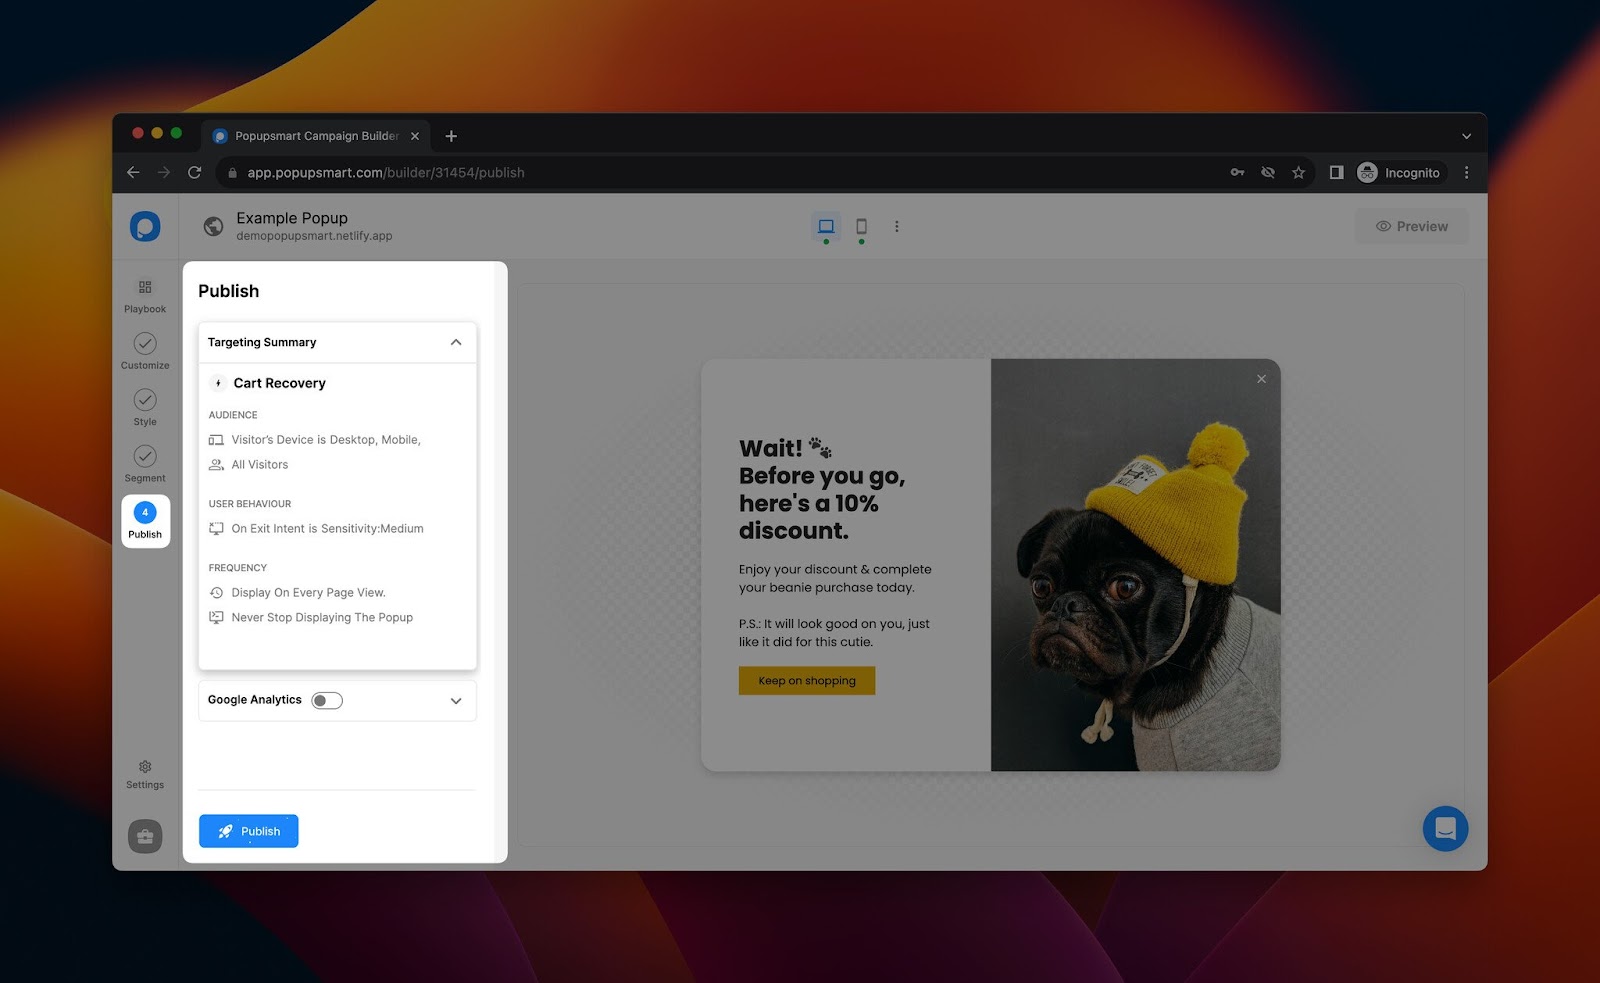
6. Publish. Review the Targeting Summary, then hit Publish.
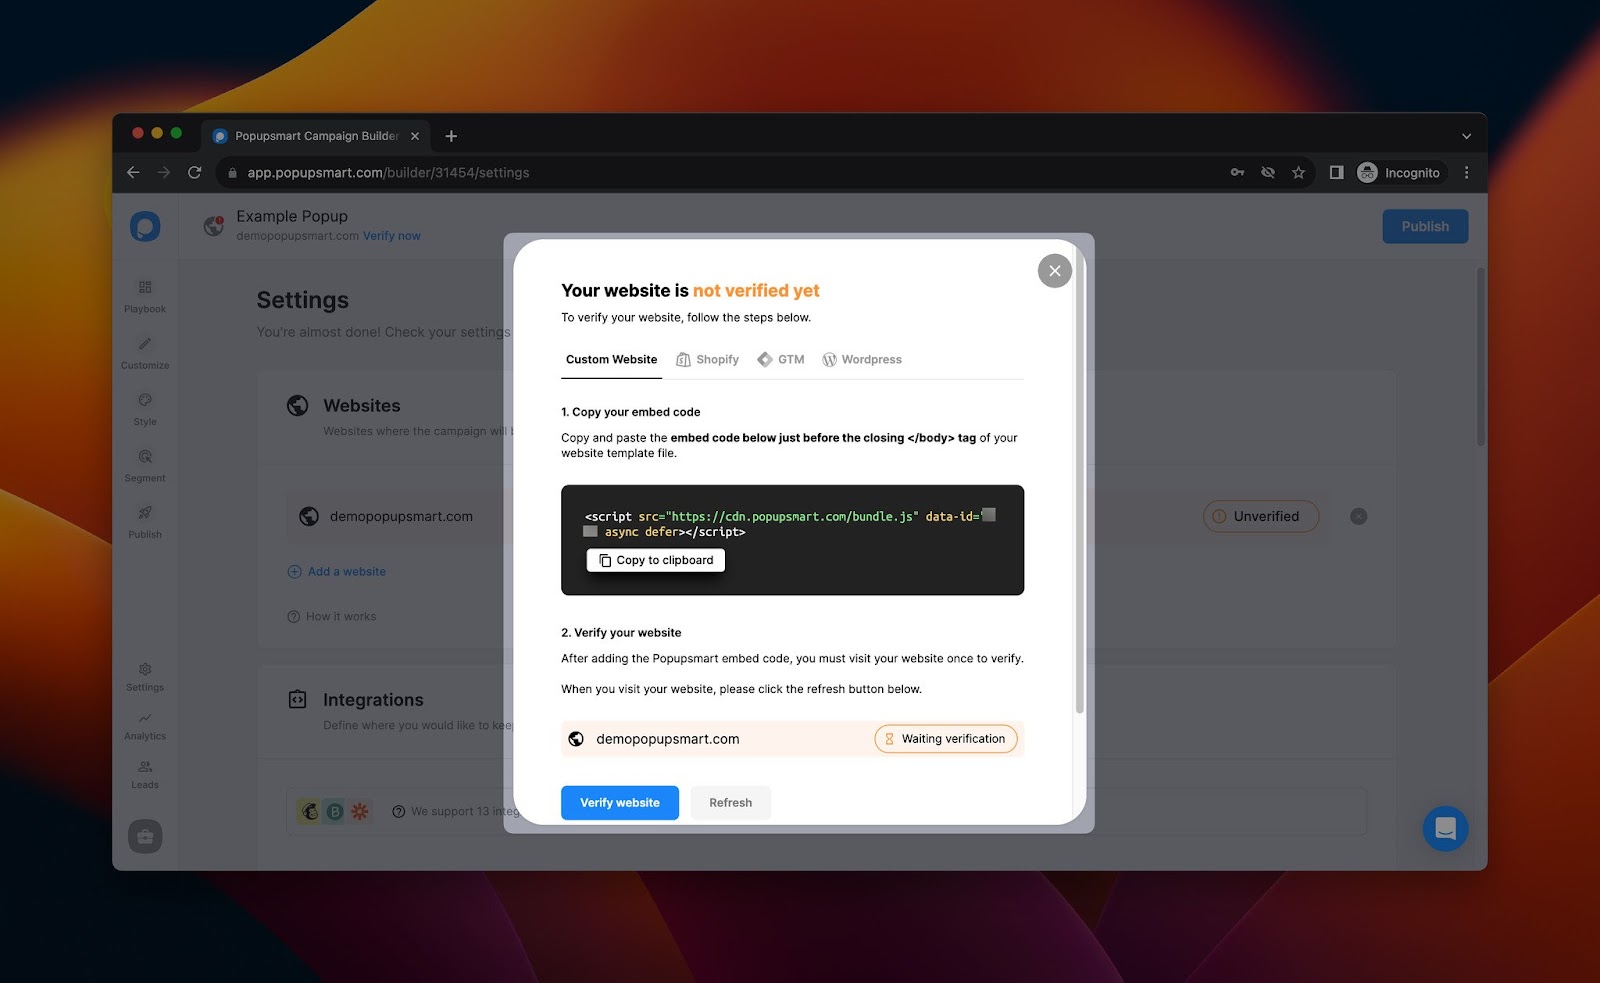
If you haven't verified your domain yet, you'll see a Verify now link. Click it, copy the embed snippet from the modal, and paste it into your site, just before the closing </body> tag of your template file. Then click Verify website, and Refresh once your site has loaded.
The embed is a JavaScript tag, but on a PHP site you just drop it into your layout file once: footer.php, app.blade.php, whatever your equivalent is. Adding it twice can stop it from working. You can also wire the install through Google Tag Manager if you prefer to keep marketing tags out of your codebase.
PHP can still steer these popups. SiteData targeting shows or hides a campaign based on values your page passes to Popupsmart with window.ps.addMeta(). A PHP page can print those values safely:
<script>
  // After the Popupsmart embed code: hand server values to SiteData targeting
  window.addEventListener('load', () => {
    window.ps.addMeta(<?= json_encode(['cartTotal' => $cartTotal], JSON_HEX_TAG | JSON_HEX_AMP | JSON_HEX_APOS | JSON_HEX_QUOT | JSON_THROW_ON_ERROR) ?>);
  });
</script>
In the campaign's Segment step, add SiteData Targeting with the property keyword cartTotal and the value to compare against. To open a campaign from a button instead, On-Click Targeting gives you a snippet for the button's click handler.
Here's what the finished popup looks like on a real site:
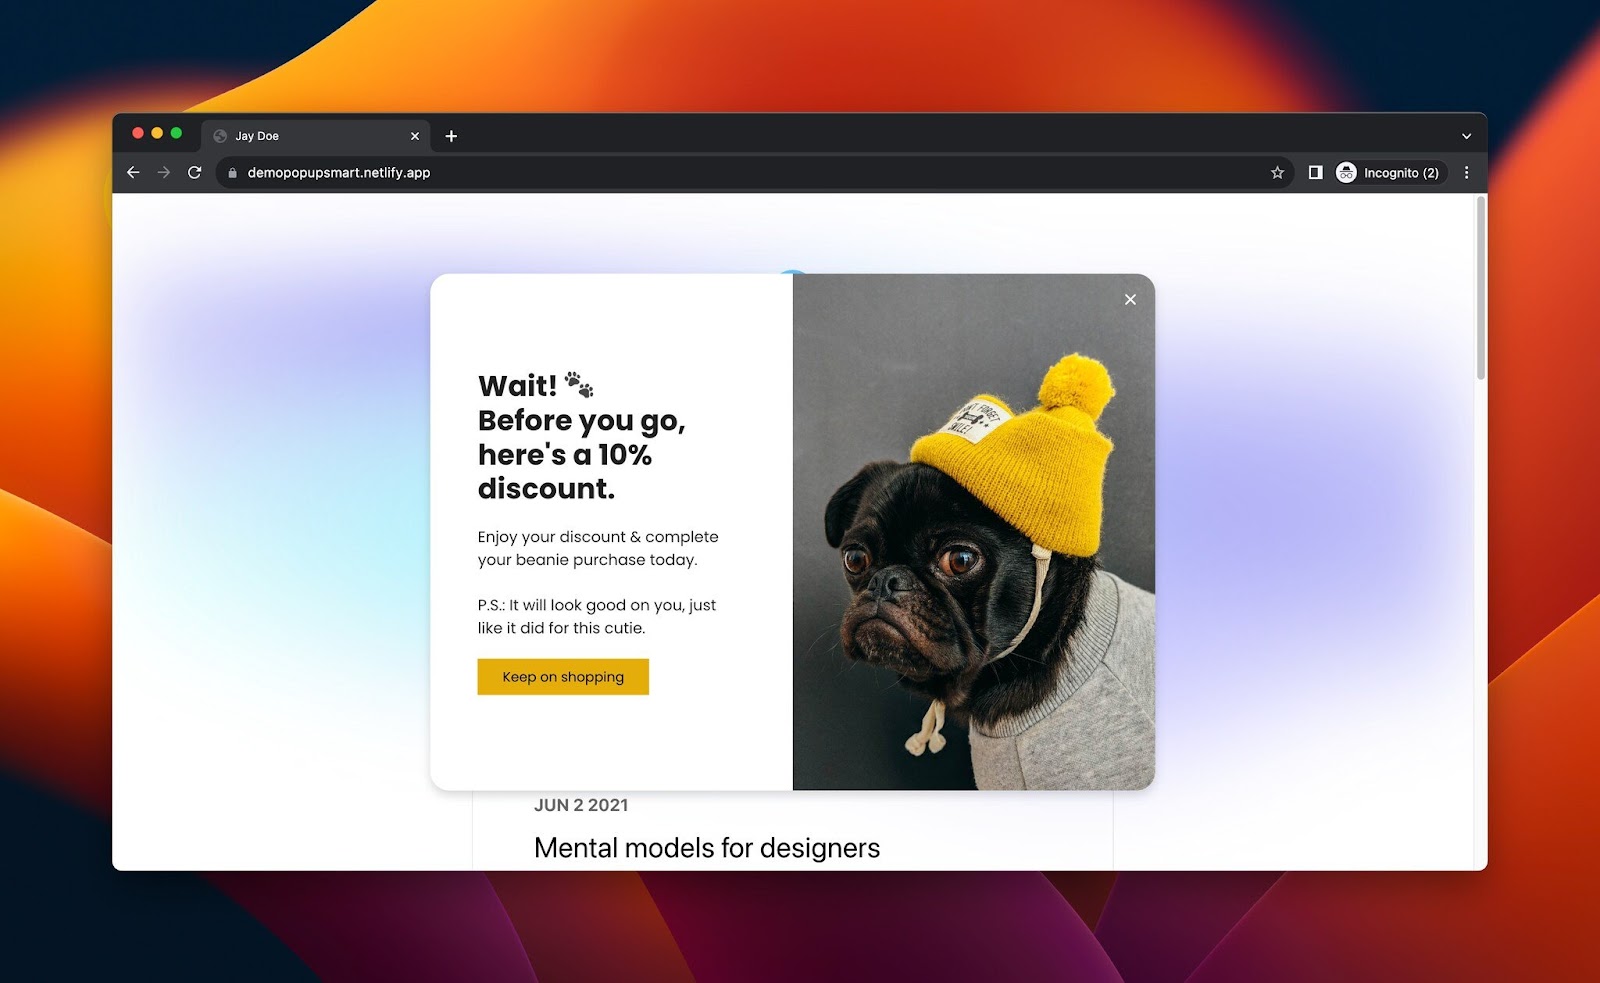
The short version: PHP popups give you server-triggered control, and the styling is yours to write. Popupsmart gives you styled, targetable popups with no backend code, and A/B testing on the Advanced plan and up. They solve different problems, and many production sites end up using both: native dialogs for in-app confirmations, a popup builder for the marketing layer.
Best Practices for PHP Popups in 2026
A few patterns separate clean implementations from the messy ones:
• Render the popup decision server-side, render the popup itself client-side. Don't try to do popup state-management in PHP. Set a flag, flash a session value, return a JSON field, then let the frontend pick it up. This is the single biggest mindset shift between 2015 PHP and 2026 PHP.
• Always pass dynamic content through json_encode() when echoing into a script tag, and through htmlspecialchars() when printing into HTML. This avoids escape-character bugs and prevents reflected XSS on user input.
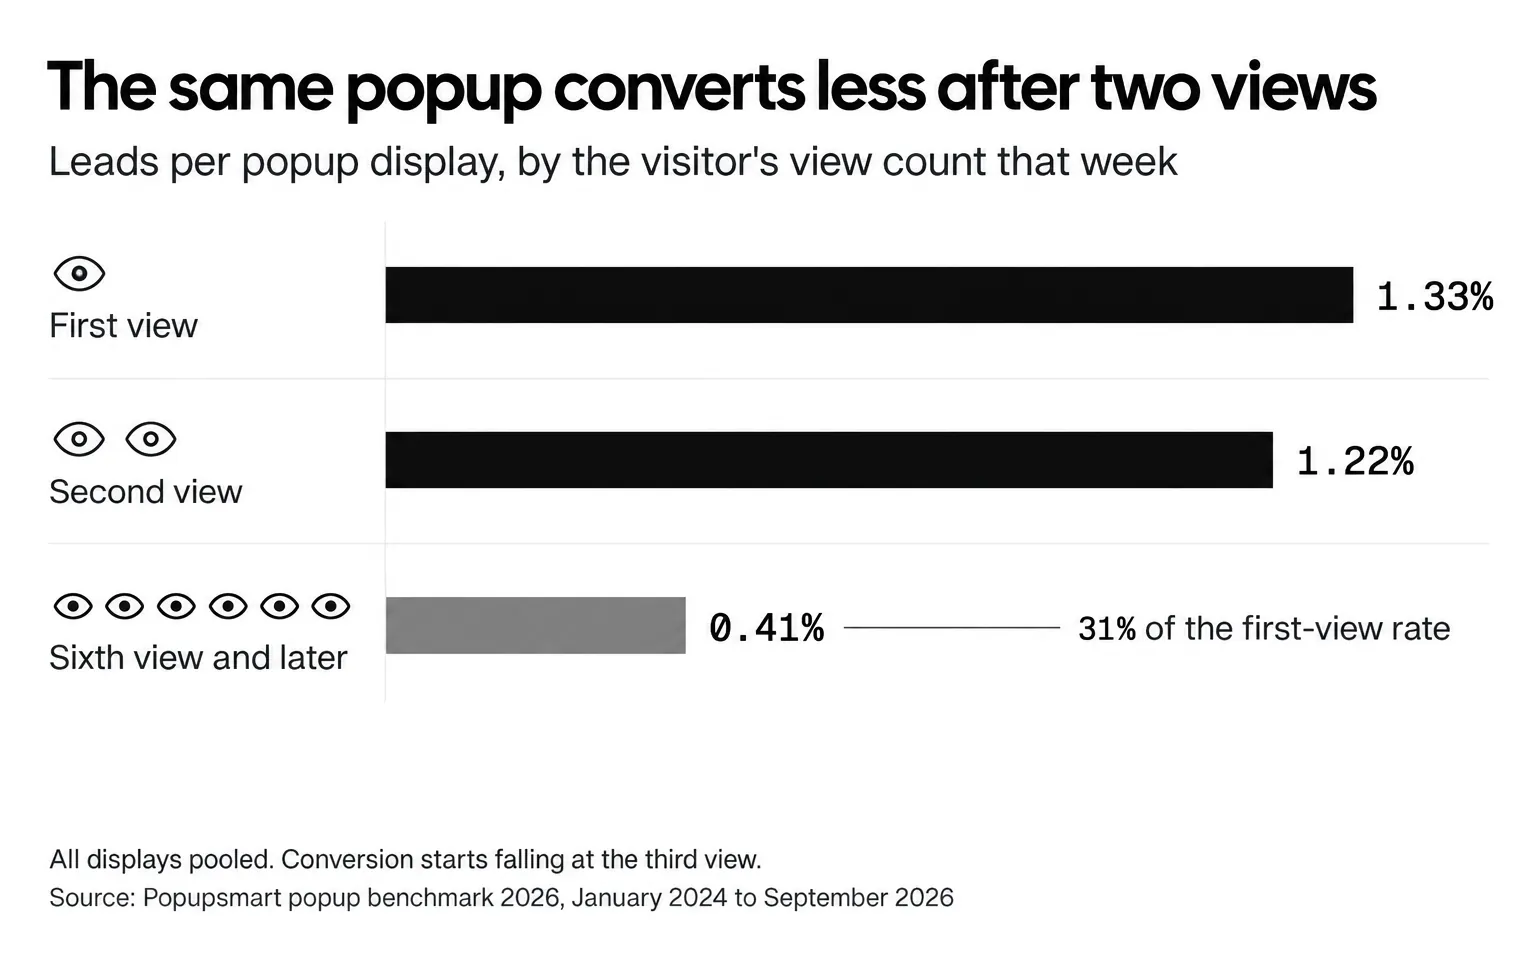
• Don't fire a popup on every page load. Wrap it in a condition that checks session state, a cookie or a database flag. Repetition costs you: in Popupsmart's 2026 benchmark, the first two times a visitor sees a popup in a week convert at similar rates (1.33% and 1.22% of displays, pooled); from the third view conversion falls, and from the sixth view it is 0.41%, 31% of the first-view rate.
• Give marketing popups a moment before they appear. In the same benchmark, popups that wait before appearing convert 0.83% vs 0.61% for popups shown the instant the page loads (median campaign); the direction holds in every year of data but the difference is not statistically reliable, so treat it as a lean, not a rule. Our popup timing guide covers delays and triggers in detail. Messages that answer something the user just did, like a save confirmation, should still appear at once.
• Reserve native dialogs for one-shot, no-style use cases. Admin tools, internal confirmations, quick error notifications. Customer-facing flows deserve a real modal: a <dialog> you style, or a popup builder.
• Test on phones. Native alert() and confirm() dialogs look and behave differently in mobile Safari and Chrome for Android than on desktop. Check that the wording fits and the flow still works, and check your <dialog> at 375px wide.
• Don't rely on window.open(). Popup blockers kill it. If you need a separate window, use a modal overlay instead.
Common Mistakes to Avoid with PHP Popups
These are the ones I see most often in code reviews and on Stack Overflow:
• Echoing JavaScript without escaping: echo "<script>alert('$message');</script>"; with $message from user input is a textbook XSS. Always json_encode() first.
• Mixing server-side state with client-side state: The result of a confirm() dialog is not available to PHP on the same request. The page is already rendered. You need a follow-up request to act on the user's choice.
• Firing popups before page render: Echoing a script at the top of a file fires the alert before the rest of the HTML loads. Either move the script to the end of the document, or wrap it in document.addEventListener('DOMContentLoaded', ...).
• Using window.open() as a popup: Browsers block almost all window.open() calls that aren't triggered by a direct user click. If your "popup" never appears in Chrome, this is almost always why.
• Forgetting accessibility: Native alert and confirm are accessible by default: screen readers announce them, Escape dismisses them. Custom modal libraries often aren't. A <dialog> opened with showModal() gets most of it for free; still give it a labelled title and test with VoiceOver or NVDA before shipping. Our popup UX design guide lists the design mistakes that hurt most.
• Treating popups as a free conversion lift: Popups work when they're targeted, timed, and offer real value. A blanket "Subscribe to our newsletter" on every page load mostly trains visitors to close it.
Measuring PHP Popup Impact on Conversions
If you're rolling out PHP popups for anything user-facing, you need a way to measure whether they're helping or hurting. Native alert() and confirm() dialogs don't emit events you can track, which is one of the biggest reasons to graduate to a real popup system once the use case crosses from internal to customer-facing.
For native dialogs, the workaround is to fire an analytics event from the same script tag that fires the popup. With Google Analytics 4 installed through gtag.js:
<?php if ($loginFailed): ?>
<script>
  gtag('event', 'popup_shown', { popup_type: 'login_error' });
  alert('Invalid credentials. Please try again.');
</script>
<?php endif; ?>
That gives you "popup_shown" counts in Google Analytics. You won't get dismissal time or interaction data, since the native dialog doesn't expose those, but you'll at least know how often the popup fires. With a <dialog>, you can also send an event from its close listener.
For marketing popups, the metrics that matter are: impressions, click-through rate on the CTA, completion rate (for forms), and lift on the downstream conversion. Most popup builders surface these as standard reports. If you're rolling your own, make sure you're at least logging impressions and conversions to the same database table, otherwise you're flying blind. Log closes too: in Popupsmart's 2026 benchmark, 40.5% of popup displays end with the visitor closing the popup (all displays pooled, February 2025 - September 2026, since close tracking began).
For a baseline, use measured data rather than a rule of thumb. Across 3,034 Popupsmart popups that ask for an email or phone number (January 2024 - September 2026, each with at least 1,000 displays and 14 active days), the median converts 0.83% of its displays into leads; the top 25% reach 1.96% and the top 10% reach 3.87%. The 2026 popup conversion benchmark report has the method. Measure your own popup per display the same way before you compare. If you're far below the median, the usual suspects are the audience (showing it to the wrong visitors), the copy (no clear value) and the timing (firing too early or too often). Don't chase the popup: fix the upstream signal.
Picking Your PHP Popup Approach
PHP popups haven't changed much under the hood in a decade, but the right way to use them in 2026 has. For server-triggered, single-message dialogs inside your app, native alert(), confirm(), and prompt() are still the fastest tool: a few lines of code, zero dependencies, accessible by default. For anything customer-facing with styling, timing, or targeting needs, you've outgrown the native dialogs: render a <dialog> from PHP, and put a proper popup system on top when you need targeting and testing.
If you're stuck on a specific use case, my recommendation is to start with the smallest version that solves the problem. Drop in alert() for the proof of concept. Watch how often it fires. Read the console for errors. If it works and nobody complains, you're done. If it doesn't scale (if you need styling, mobile layout, A/B testing, or analytics), that's the moment to graduate. Not before.
Frequently Asked Questions About PHP Popups
How do you create a popup in PHP?
You create a PHP popup by echoing a JavaScript script tag that calls alert(), confirm(), or prompt(). PHP runs server-side and can't open windows directly, so it injects the JavaScript into the page, and the browser fires the dialog. You can wrap the echo in an if statement to make the popup conditional on server state. For a styled popup, render a dialog element with escaped text and open it with showModal().
What is the difference between PHP and JavaScript popups?
JavaScript popups run entirely in the browser: the user's click or scroll triggers them, and JavaScript handles everything. PHP popups are JavaScript or HTML popups that PHP decides to render based on server-side conditions (a failed login, a database state, a session value). The dialog itself always runs in the browser. The difference is who controls the trigger: the client (pure JS) or the server (PHP).
Why doesn't my PHP popup show up?
The three most common causes are: (1) Browser pop-up blockers, which kill window.open() but not alert(), so check that you're using the right one. (2) JavaScript syntax errors caused by unescaped quotes in the echoed string, so wrap dynamic content in json_encode(). (3) The PHP condition isn't true on that request, for example because the session flash value wasn't set before the redirect.
Are PHP popups secure?
Native alert, confirm, and prompt dialogs are themselves safe: they're browser primitives. The vulnerability comes from echoing user-supplied content into the script tag without escaping. If a user types '); alert('XSS into a form and your PHP echoes it back into a popup unsanitized, you've shipped a reflected XSS bug. Always pass dynamic content through json_encode() on the way into JavaScript, and htmlspecialchars() on the way into HTML.
How do I show a PHP alert message after a form is submitted?
Process the form, store the message in the session and redirect with a 303 status (the Post/Redirect/Get pattern). On the next page, read the message, delete it from the session and render it, as an alert() through json_encode() or as a dialog element through htmlspecialchars(). The redirect stops the message from showing again, and the form from resubmitting, when the visitor refreshes.
How can you create a popup with a button click in PHP?
Strictly speaking, a button click is a client-side event, so the popup should be tied to the click handler, not to the PHP render. Render the button and a dialog element from PHP, with the message escaped inside it, then open the dialog with showModal() from an addEventListener click handler instead of an inline onclick. Our guide on building a button-click popup walks through the full pattern, including the no-code version.
Next on your reading list: